> whoami

Andrew Vinston D'Souza"Andyy"

Aspiring SOC Analyst | Threat Detection & Incident Response

Top 4% on TryHackMe · BCA @ St. Aloysius University, Mangaluru

identity.captureVERIFIED
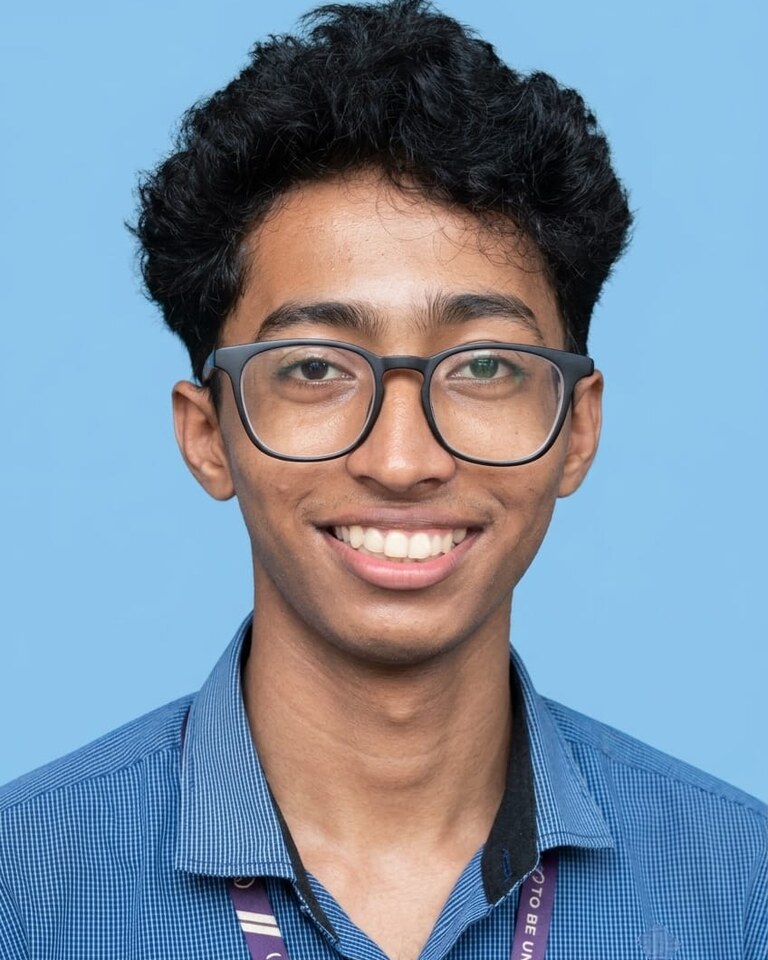
Andrew Vinston D'Souza, aspiring SOC analyst
ID: andyydz · STATUS: AVAILABLE
SOC.CORE // SECURITY SIMULATIONNORMAL
LOGSEDRIDSNETWORKCLOUDSOCCORE
  1. 01 DETECTION
  2. 02 INVESTIGATION
  3. 03 RESPONSE

SIMULATED TELEMETRY · NOT LIVE DATA

$ tail -f /var/log/andyydz.log

fetching activity…

[LOG] Completed: Greenholt v2 — phishing investigation

[LOG] Pushed 3 commits to SOC-Portfolio

[LOG] Earned: Cyber Security 101 Certificate (TryHackMe)

TRYHACKME / RANK

0

top 4%

TRYHACKME / BADGES

0

TRYHACKME / STREAK

0 days

TRYHACKME / ROOMS

0

github/andyydz fetching live stats…

rooms: Nmap · Wireshark · TCPDump · Hydra · John the Ripper · Snort (IDS Fundamentals) · Firewall Fundamentals · Hashing Basics · SIEM Introduction · Digital Forensics Fundamentals · OWASP Top 10 · Web Application Basics · Greenholt v2 (phishing investigation)

> cat about.md

01 / PROFILE

Curious about how systems work since I was a kid — that curiosity pointed itself at cybersecurity, specifically defense. I care about understanding why something breaks, not just patching it and moving on. Most days I'm in TryHackMe's SOC and Blue Team paths — log analysis, incident response sims, Splunk, Wireshark, Nmap — mapping attack behavior to MITRE ATT&CK and writing it up on GitHub as I go. Top 4% globally on TryHackMe, 116 rooms completed, 61-day streak. Looking for an internship or entry-level SOC Analyst role.

> ls skills/

> ls projects/

CASE FILE 01 · FEATURED

Security Incident & Asset Tracker

Repository
01 / problem
Small IT teams often track assets in spreadsheets and log incidents in chat, so nothing links a compromised host to the incident history behind it.
02 / approach
Built a Java + JDBC console application on MariaDB with a relational schema linking Assets↔Incidents, a DAO layer for data access, and PreparedStatement used throughout to prevent SQL injection.
03 / outcome
Assets and incidents are queryable together, with severity classification on every incident. Built and tested end to end on Kali Linux.
04 / what's next
Add analyst-facing reporting queries and export incident timelines mapped to MITRE ATT&CK techniques.

CASE FILE 02 · FEATURED

SOC-Portfolio

Repository
01 / problem
Blue Team learning is easy to collect and hard to prove — labs get completed and forgotten, with no evidence of how a detection was reached.
02 / approach
Built a repo of end-to-end SOC investigations: Splunk and ELK queries over Windows Event Logs, Wazuh alert triage, and packet captures, each documented as alert → pivot → evidence → verdict and mapped to MITRE ATT&CK techniques.
03 / outcome
A reviewable body of investigations covering phishing analysis, brute-force and persistence detection, and log-source coverage gaps — reproducible by anyone reading the writeups.
04 / what's next
Add detection rules as reusable Sigma signatures and cover cloud/identity log sources alongside endpoint telemetry.

Cybersecurity-Writeups

TryHackMe writeups on Linux, Windows, SOC workflows, and cybersecurity fundamentals.

  • TryHackMe
  • Writeups
  • Linux
  • Windows

Cisco-Network-Defence

Notes, labs, and Packet Tracer exercises from the Cisco Networking Academy Network Defense course.

  • Cisco
  • Packet Tracer
  • Network Defense

> cat certifications.tsv

CERTIFICATIONISSUERDATE
✓Foundations of CybersecurityGoogle / CourseraJun 2026
✓Play It Safe: Manage Security RisksGoogle / CourseraJul 2026
✓Pre Security CertificateTryHackMeMay 2026
✓Cyber Security 101 CertificateTryHackMeJul 2026

IN PROGRESS / Currently working on: Google Cybersecurity Certificate — Course 2, and TryHackMe's SOC Level 1 path

> cat experience.log

SOC & Blue Team Trainee

Self-Directed Practice, TryHackMe

Feb 2026 – Present

  • – Practicing SOC workflows via SOC Level 1, Pre Security, and Blue Team paths.
  • – Phishing email analysis, network traffic inspection, threat intel correlation.

> cat volunteering.log

Technical Volunteer

CODESPRINT National-Level Hackathon, St. Aloysius

Jan 2026

  • – Technical coordination and participant support.
  • – Implemented a bridge-based network fix during the event.

> cat testimonial.txt

RECOMMENDATION / VERIFIED ATTRIBUTION

“I've had the pleasure of teaching Andrew during his BCA program at St. Aloysius. He consistently stood out — not just academically, but for his proactive approach to learning and technology, and his strong problem-solving skills in inter-college hackathons. He collaborates effectively under pressure and thinks on his feet. I highly recommend him for any technical roles or projects he pursues.”

Rishal Noronha
Assistant Professor, St. Aloysius (Deemed to be University), Mangaluru

RECOMMENDATION / VERIFIED ATTRIBUTION

“Andrew is a dedicated and curious cybersecurity enthusiast with a strong passion for learning and developing his skills. As a classmate, I’ve seen his commitment to cybersecurity and continuous improvement. I’m confident he’ll be a great asset to any cybersecurity team.”

Prajwal V Raghavendra
Classmate / Peer

Computer Science Student | Aspiring DevOps Engineer | Backend Development & AI Enthusiast | Seeking Internship

> ./contact.sh

MESSAGE REQUEST

Fields are validated before submission.